shim-cli
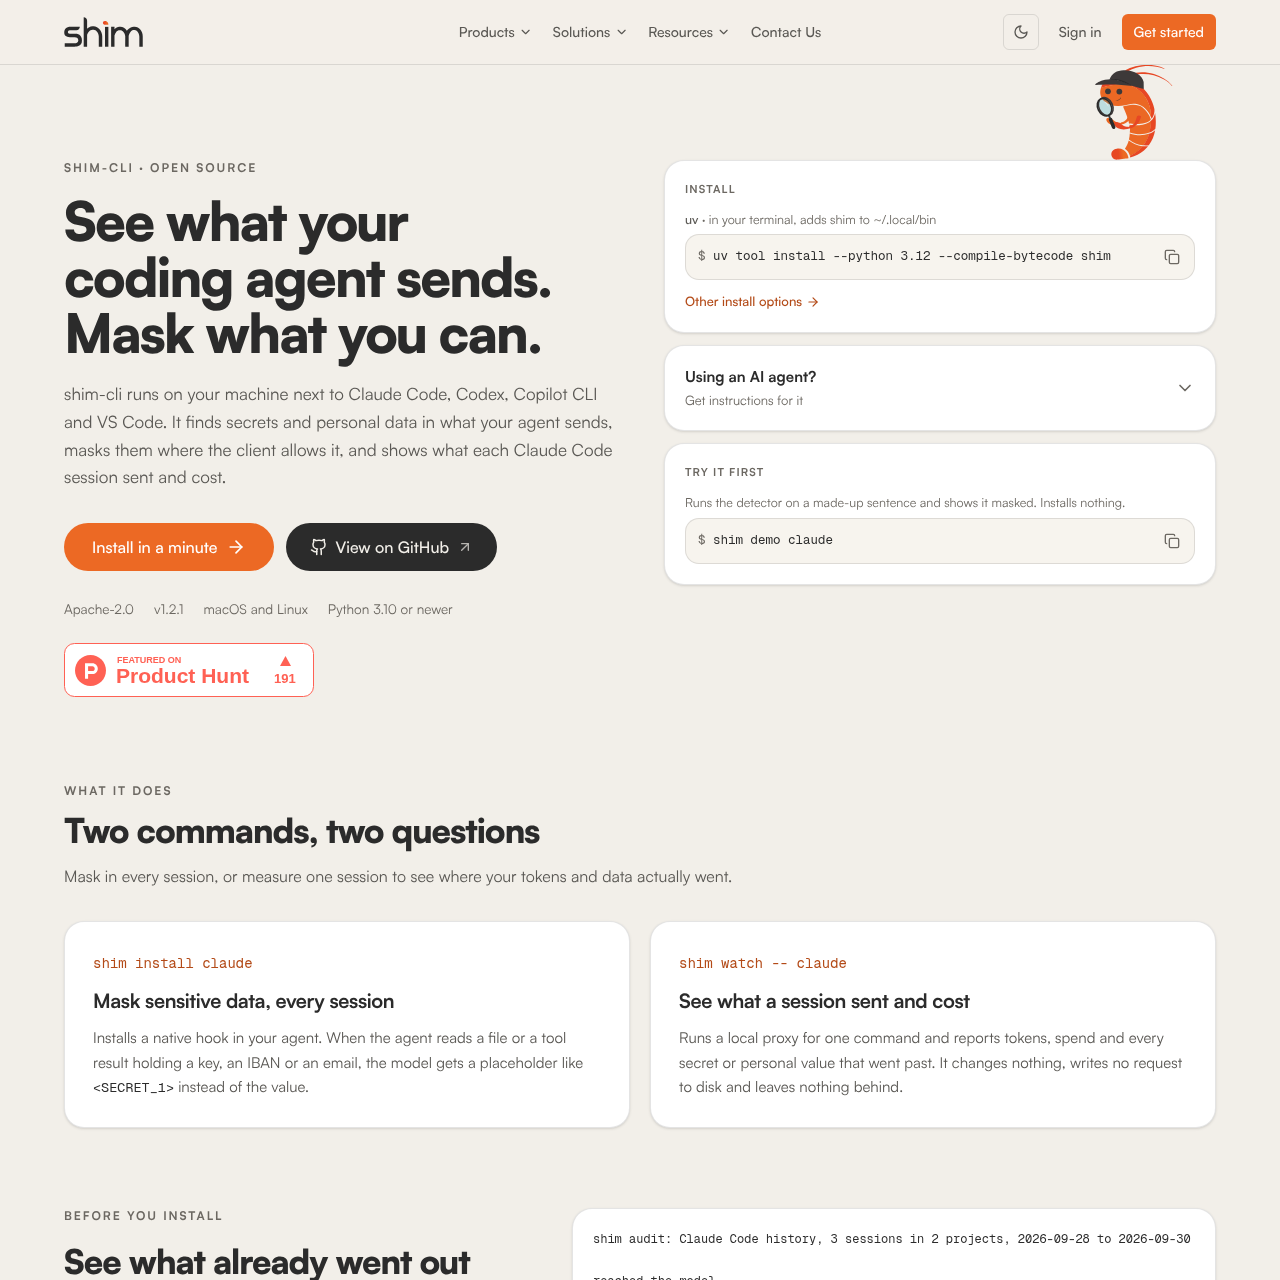
shim-cli is an open-source local security tool that detects and masks sensitive data in coding agent workflows such as Claude Code.
What the product does and how it is positioned
shim-cli runs locally alongside developer agents like Claude Code, Codex, Copilot CLI, and VS Code on macOS and Linux systems.
It identifies sensitive information including credentials, personal identifiers, and configuration secrets, masking values before model dispatch where agent hook architectures allow.
Source-supported ways to use the product
Helping reduce accidental exposure of credentials and personal data when coding agents read local files or tool results.
Scanning stored Claude Code session logs to evaluate token counts, spend, and past exposures across local projects.
Observing single-command agent executions through a local proxy to monitor token usage and transit of sensitive values.
The documented workflow, where available
Install shim into the local terminal environment using uv or pipx with Python 3.10 or newer.
Run the built-in demo command on sample text to verify masking behavior without altering system files.
Install the native hook or configure the Claude Code marketplace plugin to hook into agent operations.
Execute the diagnostic doctor command and confirm active hooks inside the agent session.
The protection level provided by shim-cli varies according to the architectural constraints of each supported coding client. While Claude Code allows native hooks to rewrite file contents and tool outputs into placeholders before reaching language models, Codex does not allow hooks to rewrite prompts entered directly by the user.
Where direct masking is unsupported by the host agent, shim-cli provides alert reporting and optional enforce modes to block operations before execution. In VS Code, files read by agents are not visible to the tool, and tool traffic in Codex and Copilot CLI remains uninspected.
Checks to run with your own material and workflow
What was checked and when
Answers based on the source-checked product record
shim-cli supports macOS and Linux environments running Python 3.10 or newer. Windows is unsupported, and WSL has not been verified.
Prompts typed directly into Claude Code are not masked because the client does not permit hooks to rewrite them, though they can be reported or blocked in enforce mode.
The tool detects emails, phone numbers, credit cards, verified IBANs, Turkish IDs and tax IDs, API keys, passwords, database URIs, IP and MAC addresses, US SSNs, and custom regex patterns.
No, shim-cli requires no user accounts or API keys, adds zero telemetry, and performs all detection and proxying locally on the user machine.
The audit command inspects Claude Code historical session logs stored on the local disk to calculate exposure metrics by project and source without modifying or transmitting data.