VibeDefend by CybeDefend favicon

VibeDefend by CybeDefend

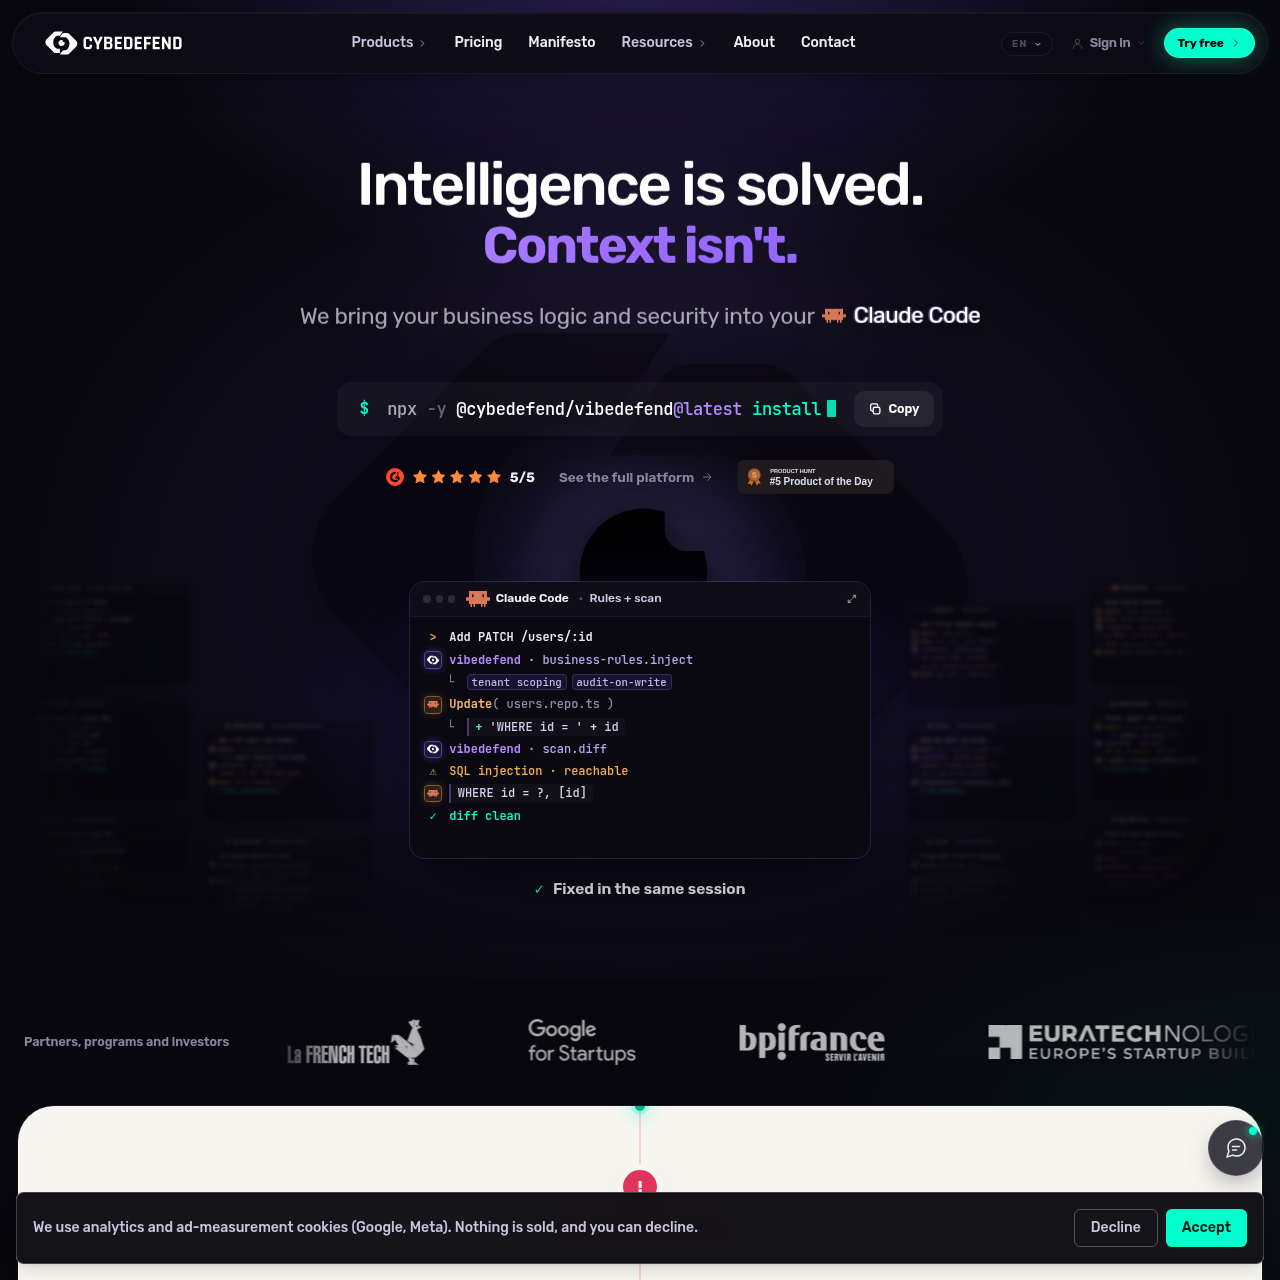
VibeDefend by CybeDefend is an agent-time security tool that injects business rules, guards shell actions, and scans code diffs across AI coding environments to catch vulnerabilities before commit.

Code & ITInjecting mined business rules and…Blocking hazardous shell and SQL…Detecting SQL injection, hardcoded…Guarding Model Context Protocol server…
VibeDefend by CybeDefend product interface screenshot
Estimated monthly visits
1K
Data period:
Listed on AIToolly

What Is VibeDefend by CybeDefend? Product Overview

What the product does and how it is positioned

VibeDefend by CybeDefend is designed to protect software development workflows that utilize AI coding agents. Installed on developer workstations via a single command, it integrates directly with coding environments to enforce project context, security standards, and business logic before code is committed or pull requests are submitted.

The tool combines proprietary analysis engines with established open-source security scanners covering static analysis, software composition analysis, infrastructure as code, and secret detection. In addition to scanning diffs, VibeDefend features an action guard that intercepts dangerous terminal commands and monitors interactions with Model Context Protocol servers.

What Can You Use VibeDefend by CybeDefend For?

Source-supported ways to use the product

helping reduce Insecure AI Code Generation

Development teams can scan AI-generated diffs in real time for vulnerabilities like SQL injection, exposed API keys, and vulnerable third-party dependencies before changes are committed.

Blocking Hazardous Shell Operations

Organizations can enforce terminal safeguards that stop coding agents from executing destructive commands, such as live database schema drops, unconstrained deletions, or unauthorized sudo operations.

Enforcing Business and Compliance Rules

Teams can inject custom business logic and regulatory standards like GDPR and ISO 27001 into AI agent contexts to ensure generated endpoints adhere to authorization and logging requirements.

How to Use VibeDefend by CybeDefend

The documented workflow, where available

  1. 1

    Installation

    The developer executes the installation command via npx to detect and configure AI coding agents present on the local machine.

  2. 2

    Rule Injection

    VibeDefend injects mined business logic and compliance standards directly into the AI agent prompt session.

  3. 3

    Live Guarding and Scanning

    As the agent generates code and shell commands, the action guard inspects terminal executions and scans diffs for security vulnerabilities.

  4. 4

    Remediation

    Findings and fixes are presented directly within the agent session or team dashboard, prompting the agent to rewrite insecure lines before pull requests are created.

Agent Guarding and Scanning Architecture

VibeDefend operates directly within developer environments to intercept actions taken by autonomous coding assistants. Rather than relying solely on static configuration files, the platform injects business rules and compliance requirements into the agent session while monitoring executed commands in real time.

The underlying architecture integrates CybeDefend proprietary analysis engines with established open-source tools including Opengrep for code analysis, Trivy for containers and infrastructure, Syft and OSV for dependencies, Gitleaks for secret detection, and Checkov and KICS for infrastructure as code. This multi-layered approach verifies that both command execution and generated diffs adhere to organizational policies.

  • Monitors Model Context Protocol interactions to help reduce prompt injection and tool hijacking.
  • Blocks unauthorized terminal commands including live database drops and destructive file system operations.
  • Scans code modifications against OWASP, SOC 2, GDPR, and ISO 27001 standards before pull requests are submitted.

What to Test Before Choosing VibeDefend by CybeDefend

Checks to run with your own material and workflow

  • Verify that the local installation command successfully detects all target AI coding agents and development environments on the host system.
  • Check how the action guard handles high-risk terminal commands, such as database drops or unconstrained file deletions.
  • Confirm whether injected custom business logic and compliance rules are correctly reflected in AI-generated diffs.
  • Review the current status of compliance certifications, including the ongoing SOC 2 Type II audit.

VibeDefend by CybeDefend Sources and Last Checked

What was checked and when

Last checked
Category
Code & IT

VibeDefend by CybeDefend Frequently Asked Questions

Answers based on the source-checked product record

How is VibeDefend installed on a developer machine?

VibeDefend is installed by executing a single command via npx, which automatically identifies and connects to supported coding agents present on the system.

Which security scanning engines are integrated into VibeDefend?

The platform pairs proprietary CybeDefend engines with open-source tools including Opengrep, Trivy, Gitleaks, Checkov, KICS, Syft, and OSV across code, secrets, containers, and infrastructure.

How does the action guard prevent system damage?

The action guard intercepts terminal executions initiated by AI agents, blocking dangerous operations such as live database schema drops, destructive sudo commands, and unverified package installations.

What compliance frameworks does VibeDefend reference?

The system incorporates rules and checks based on OWASP standards, SOC 2, GDPR, and ISO 27001, with an official SOC 2 Type II compliance audit currently under way.

Does VibeDefend inspect interactions with Model Context Protocol servers?

Yes, VibeDefend monitors Model Context Protocol tool usage during agent sessions to guard against tool hijacking and unauthorized data transfers to external repositories.

Explore other recently added tools in the same category.