Pushary for Teams
Pushary for Teams is an approval and auditing layer for AI coding agents that pauses risky commands for human sign-off and logs every decision across the team.
What the product does and how it is positioned
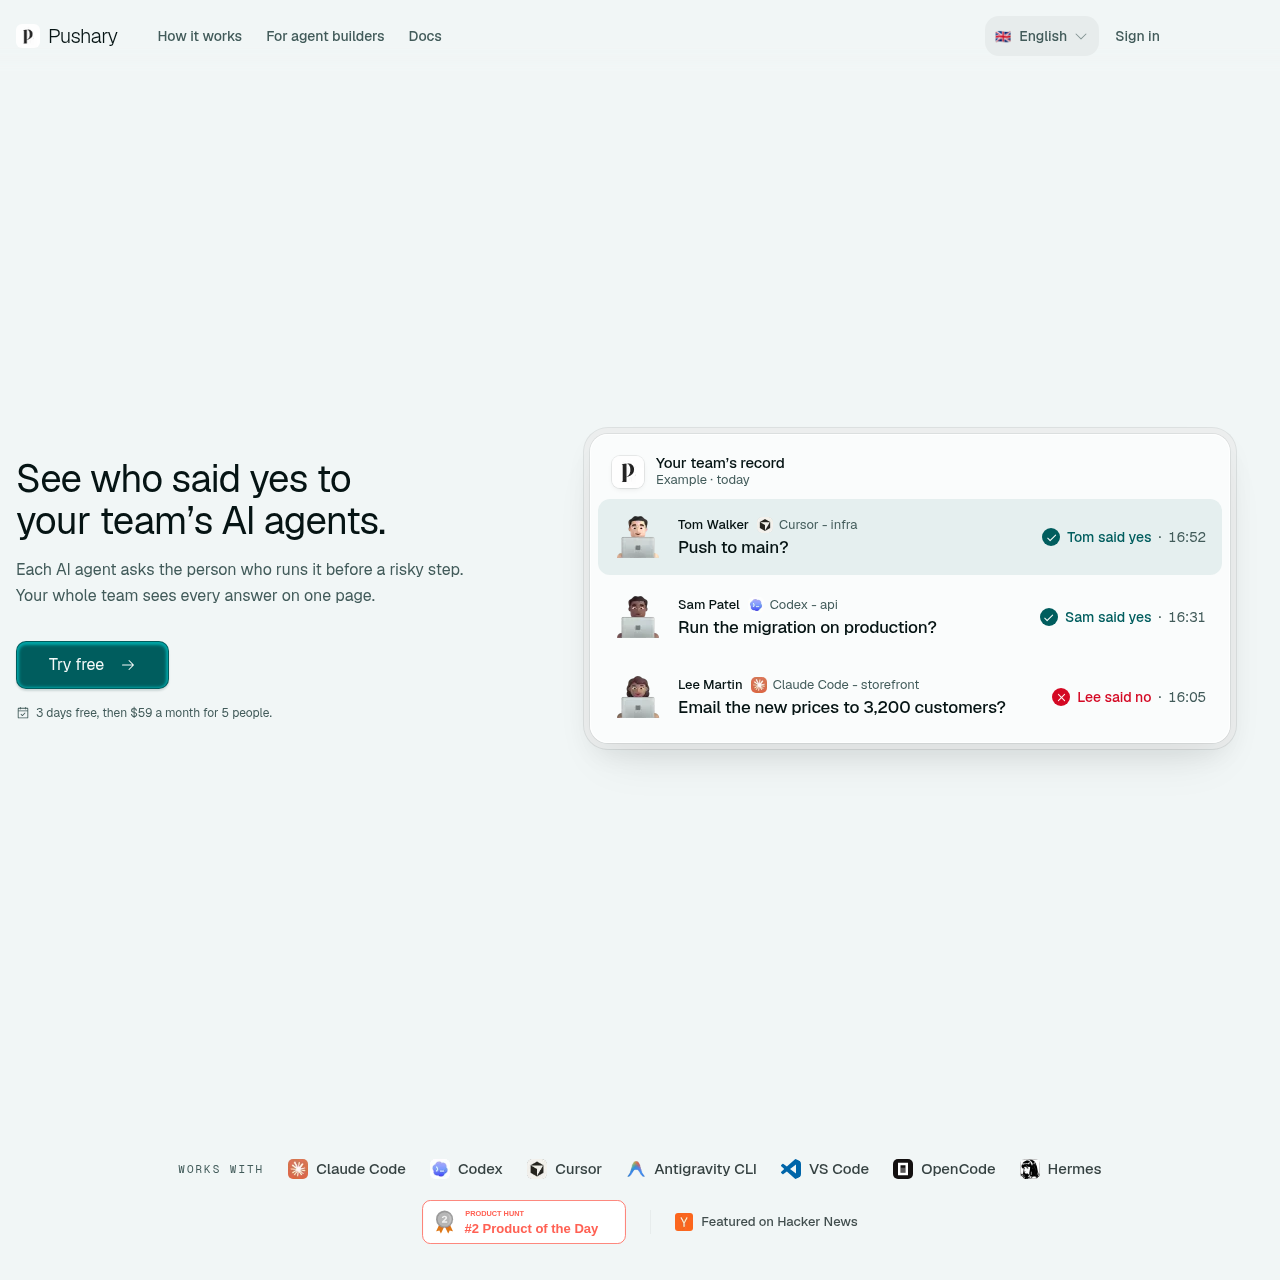
Pushary for Teams is an operational oversight tool designed to manage actions taken by autonomous coding and terminal agents. When an integrated AI agent attempts to execute a high-risk operation, such as a database migration or a direct repository push, the system pauses execution to request approval from a human operator.
Responses given via Mac desktop or mobile notifications are recorded in a centralized dashboard visible to the entire team. This activity log tracks which agent initiated the request, what action was attempted, who answered, and the exact timestamp, allowing teams to audit agent behavior and route specific tool authorizations to designated personnel.
Source-supported ways to use the product
Require explicit human confirmation before an AI agent runs database migrations or pushes changes to production branches.
Review the centralized log to determine which agent initiated an action, who approved it, and when execution took place during post-mortems.
The documented workflow, where available
Connect the Mac application or command-line interface, then pair the mobile application.
Add collaborators to the workspace so each member links their own client applications.
Run an agent command that automatically pauses before sensitive steps like code pushes or migrations.
Approve or deny the paused action from the Mac interface or mobile lock screen.
View team-wide responses on the shared log or define pattern-based routing rules to direct sensitive steps to designated leads.
Pushary for Teams intercepts terminal commands from supported AI agents such as Cursor, Codex, and Claude Code before execution occurs. When an agent attempts a sensitive command, execution is halted until an explicit approval or denial is submitted via the Mac desktop interface or a mobile alert.
All decisions are indexed in a 365-day team log that attributes each action to the initiating agent, the targeted repository, and the individual approver. Teams can export these audit records in CSV or JSON formats and configure pattern-based routing rules to direct sensitive repository operations to designated team leads.
Checks to run with your own material and workflow
What was checked and when
Answers based on the source-checked product record
The platform integrates with Claude Code, Codex, Cursor, Antigravity CLI, VS Code, OpenCode, and Hermes.
Prompts appear directly on the Mac desktop interface or on a user's mobile phone lock screen, allowing approval or denial from either location.
Yes, teams can establish routing rules based on tool patterns and repositories so specific sensitive actions require approval from a designated lead rather than the agent runner.
The team record retains event history, including who requested an action, who responded, and the timestamp, for 365 days.
Activity logs and follow-up entries can be exported in either CSV or JSON formats for retrospective analysis.