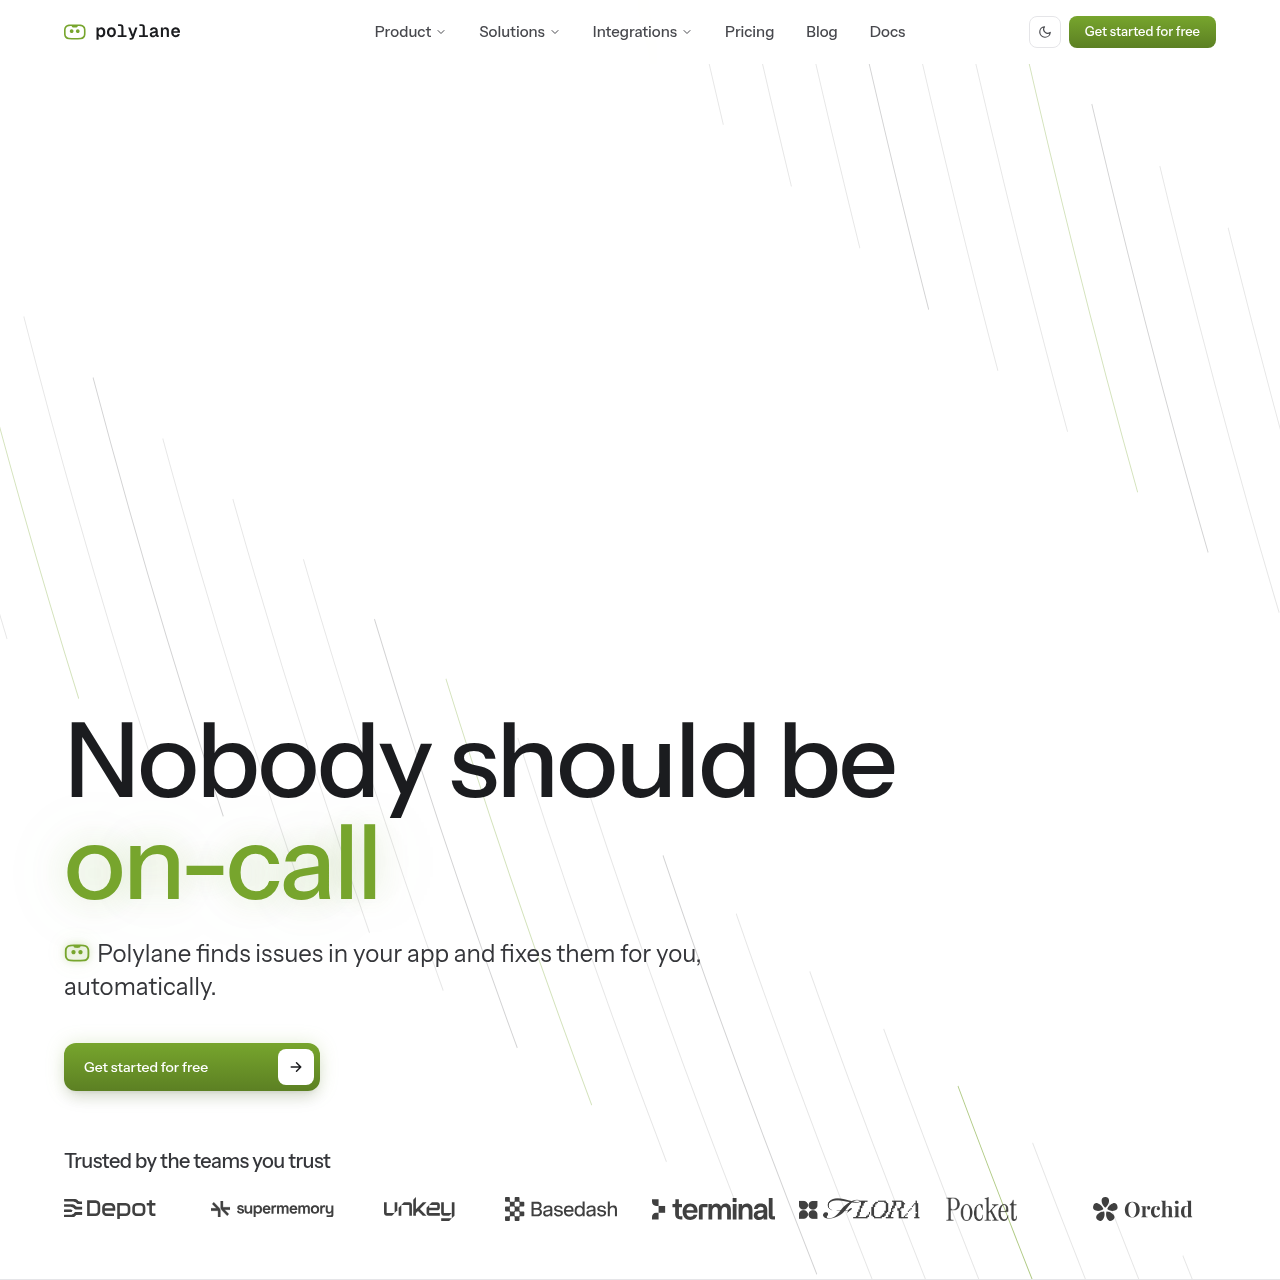
Polylane connects cloud infrastructure with application code to investigate production anomalies, generate pull request fixes, and review changes against live telemetry.
Polylane is an automated incident investigation and remediation platform that bridges production telemetry and application source code. By assembling services, repositories, and cloud resources into a unified context graph, the platform maps system relationships and traces performance anomalies back to underlying commits or configuration settings.
Beyond generating automated code fixes for active incidents, Polylane inspects proposed pull requests against live operational metrics to help reduce disruptive changes from reaching production. It also functions as an interactive diagnostics assistant in team chat and provides a contextual data layer to external AI coding agents via MCP and CLI tooling.
What Can You Use Polylane For?
Source-supported ways to use the product
Automated Incident Remediation
Triaging observability alerts, tracing performance degradation to code or configuration origins, and opening pull requests with verified fixes.
Pre-Deployment Operational Risk Analysis
Reviewing bot and engineer pull requests against live production telemetry to help reduce table-locking migrations and capacity bottlenecks.
Conversational Systems Diagnostics
Answering developer questions in Slack about latency spikes, queue saturation, and root causes associated with recent deploys.
How to Use Polylane
The documented workflow, where available
1
Alert Ingestion and Incident Triage
Ingests alerts and telemetry spikes from monitoring platforms, grouping repetitive firings into single incidents based on baseline thresholds.
2
Context Graph Investigation
Traces the anomaly across the connected context graph to inspect dependent cloud resources, queue metrics, and recent code deployments.
3
Pull Request Generation
Assembles a remediation pull request containing code adjustments, test coverage, and documentation for human review and merging.
Telemetry-Informed Remediation and Code Review
Polylane links live operational telemetry to application codebases to diagnose active issues and catch deployment risks before they impact production. When an incident occurs, the platform correlates alert occurrences against baseline performance to isolate the root cause, such as misconfigured connection pools or downstream saturation. It then executes a fix run that generates a complete pull request containing source code changes, automated tests, and updated runbooks.
In addition to remediation, the platform provides guardrails for ongoing development by evaluating proposed code changes against active production traffic. For example, when a pull request introduces database migrations on high-throughput tables, Polylane assesses the operational write load and flags non-concurrent indexing operations that could cause severe locks, blocking merge checks until safe migration patterns are implemented.
Automated incident investigation linking monitoring alerts to specific commits and infrastructure states.
Generation of pull requests with code fixes, test fixtures, and documentation updates.
Answers based on the source-checked product record
What core function does Polylane provide?+
Polylane detects and investigates production issues across code and infrastructure, automatically assembling and submitting pull requests to fix them.
How does Polylane assess code changes before they reach production?+
Polylane reviews pull requests against live telemetry, warning developers and blocking merges if proposed changes introduce locks or degrade performance under current workloads.
Can external AI coding agents use Polylane?+
External AI coding tools can query Polylane for operational context, topology maps, and log data using either the Model Context Protocol or the command-line interface.
Does Polylane apply modifications directly to production environments?+
Polylane packages fixes into pull requests with investigations, timelines, and tests, allowing engineers to review, dismiss, or merge changes rather than deploying automatically.
What security standards and encryption protocols are used by Polylane?+
Polylane holds SOC 2 Type II and ISO 27001:2022 certifications, isolates data per organization, and secures data with AES-256 at rest and TLS 1.2+ in transit.
More Code & IT AI tools
Explore other recently added tools in the same category.