Inferock
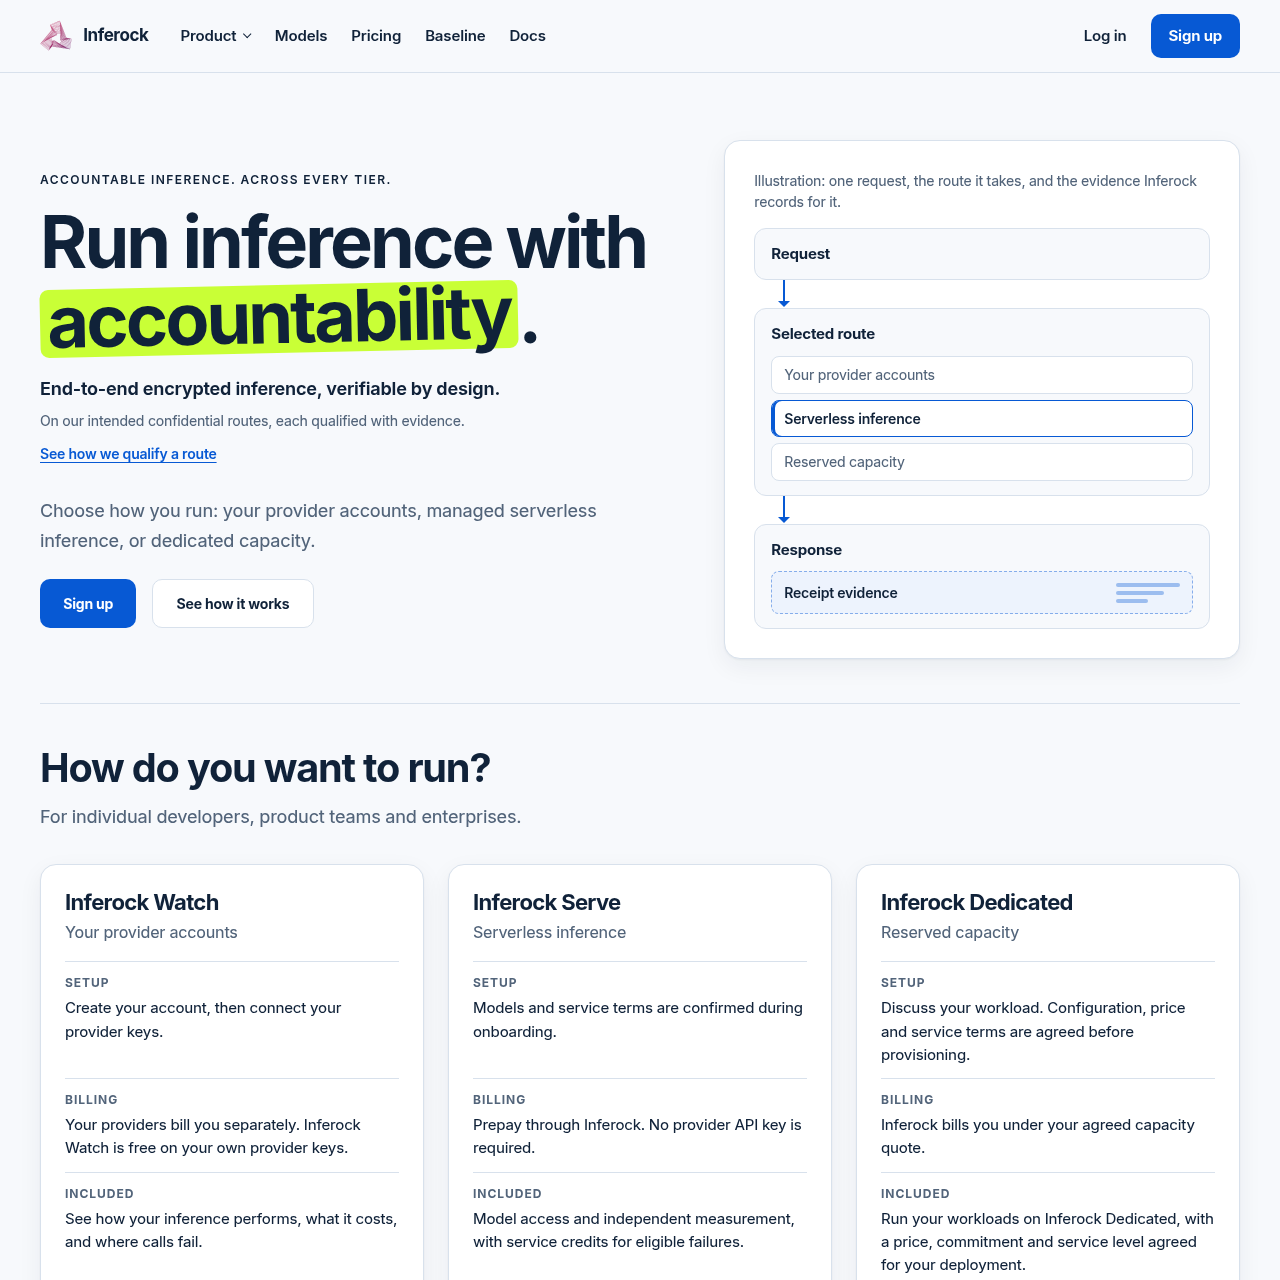
Inferock provides model routing, response measurement, and failure tracing across serverless setups, dedicated capacity, and user provider accounts.
What the product does and how it is positioned
Inferock is an inference platform that allows engineering teams to execute model calls, evaluate returned completions, and inspect failures across distinct deployment routes. Users can connect their own provider keys, deploy through serverless inference, or provision reserved dedicated capacity.
The platform records timing, usage, and output check results alongside model responses. For security-focused workloads, Inferock supports qualified confidential routes designed to preserve end-to-end encryption between the client and verified compute environments.
Source-supported ways to use the product
Validating that model completions meet application requirements, such as schema field presence, and recording failure evidence when checks fail.
Routing sensitive inference calls through qualified, verified compute environments designed to decrypt content only within the workload.
Directing calls across user-owned provider accounts, managed serverless infrastructure, or reserved dedicated capacity tiers.
The documented workflow, where available
Route requests through Inferock using external provider API keys, managed serverless inference, or reserved dedicated capacity.
Validate responses against application criteria while collecting quality findings, timing, usage metrics, and cost data.
Trace recorded application-level failures to the underlying call and review the captured diagnostic evidence.
Inferock couples inference execution with response-level measurement. When an application submits a request, the platform inspects the completion against required criteria, such as mandatory fields in structured outputs. Recorded call data pairs schema check failures with execution timing and resource usage, allowing operators to diagnose incomplete or malformed completions.
For workloads requiring isolation, Inferock outlines an intended confidential routing model. In this architecture, payload data is encrypted end to end between the customer client and a verified confidential workload where compute executes. Qualification of each confidential path depends on specific evidence gathered for the exact model and deployment setup, and this protection does not apply to regular provider-key routing.
Checks to run with your own material and workflow
What was checked and when
Answers based on the source-checked product record
Inferock supports three execution routes: running calls using your own provider keys through Inferock Watch, using managed serverless inference through Inferock Serve, or running on reserved capacity via Inferock Dedicated.
No, Inferock records output checks such as missing required fields, but the documentation notes that answer correctness requires separate evaluation.
The intended confidential route is designed to encrypt content end to end between the customer client and a verified confidential workload, where the model decrypts and processes content within the isolated environment.
No, the intended confidential route protection does not apply to ordinary Inferock Watch connections, and each confidential route requires qualification evidence for its specific model and configuration.
The Inferock documentation references inferock-bench as a source-available measurement tool related to its benchmarking and accountability framework.