
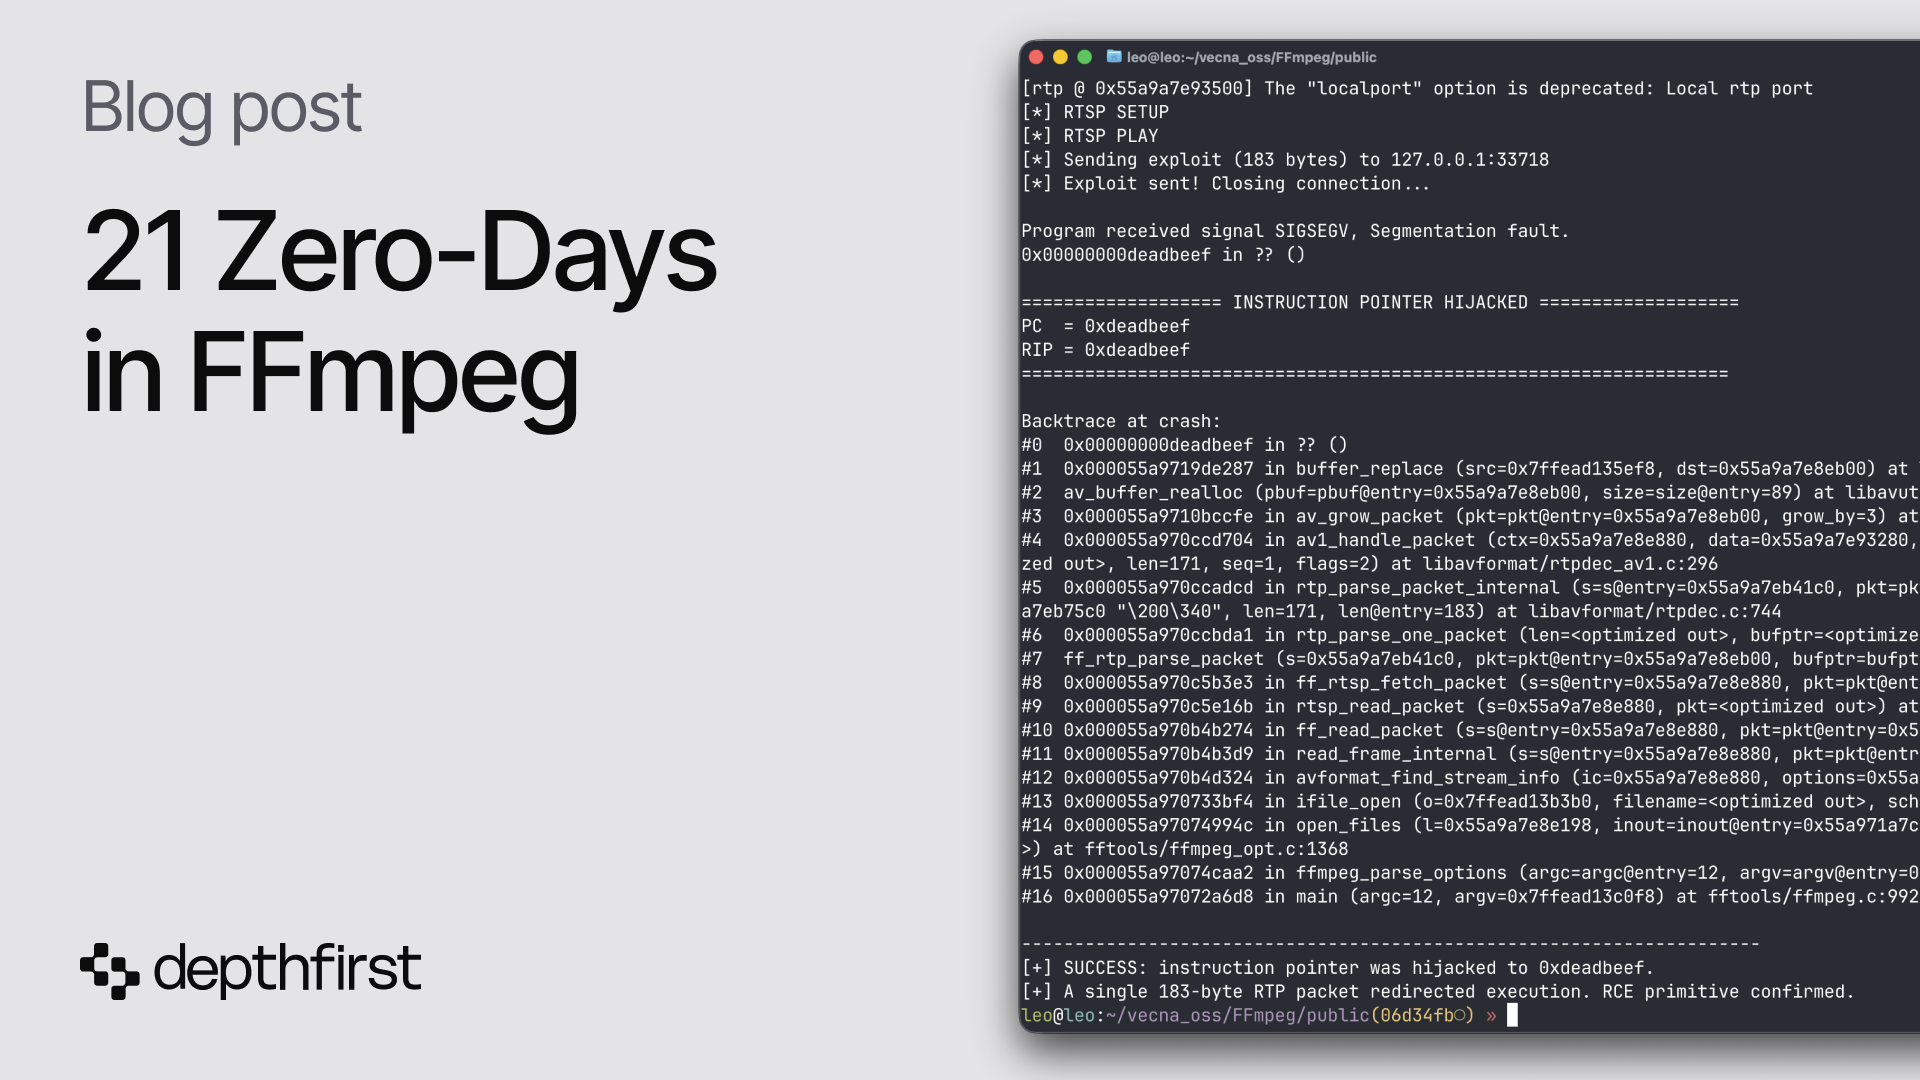
Autonomous AI Agent Discovers 21 Zero-Day Vulnerabilities in FFmpeg Media Library Following Google and Anthropic Audits
A production autonomous security agent developed by depthfirst has identified 21 previously unknown zero-day vulnerabilities within FFmpeg, a critical media processing library used globally. This discovery follows recent security analyses by Google’s Big Sleep team and Anthropic’s Mythos model. The depthfirst agent not only identified these flaws—some of which have existed in the codebase for up to 20 years—but also produced concrete, reproducible Proof of Concept (PoC) inputs and demonstrated a Remote Code Execution (RCE) exploit primitive. Operating at a significantly lower cost than traditional methods ($1,000 vs. $10,000), this breakthrough highlights the increasing capability of AI-driven security systems to audit complex, hardened C codebases that underpin modern digital infrastructure.
Key Takeaways
- Massive Discovery: A total of 21 new zero-day vulnerabilities were identified in FFmpeg by an autonomous security agent.
- Long-Term Latency: Several of the discovered security flaws had remained undetected in the codebase for 15 to 20 years.
- Actionable Results: The AI agent moved beyond theoretical discovery to produce concrete, reproducible Proof of Concept (PoC) inputs and an RCE exploit primitive.
- Cost Efficiency: The automated analysis was completed at a fraction of the cost of other methods, totaling approximately $1,000 compared to $10,000.
- Critical Infrastructure Risk: As a library with 1.5 million lines of code used in browsers and streaming platforms, FFmpeg remains a primary target for zero-click attacks.
In-Depth Analysis
The Challenge of Securing Hardened Codebases
FFmpeg stands as one of the most widely deployed software libraries in the world, serving as the backbone for media processing in web browsers and major streaming infrastructure. Its scale is immense, comprising roughly 1.5 million lines of heavily optimized C code designed to parse hundreds of complex media formats. Because it routinely handles untrusted, complex media data, it is inherently a high-stakes target for security researchers and malicious actors alike.
Historically, FFmpeg has been subjected to over two decades of intense security scrutiny, including relentless fuzzing and manual audits. Despite this hardened status, the discovery of 21 new zero-days suggests that traditional security measures may have reached a plateau. The fact that some of these vulnerabilities have been latent for up to 20 years indicates that even the most scrutinized open-source projects can harbor deep-seated flaws that elude standard detection methods. This highlights a significant gap in the industry's ability to secure legacy codebases that continue to power modern digital life.
The Evolution of AI-Driven Security Auditing
The research conducted by depthfirst follows recent milestones set by Google’s Big Sleep team, which found 13 vulnerabilities, and Anthropic’s Mythos model. These efforts demonstrate that advanced AI models are increasingly capable of reasoning through dense, low-level C code. However, the depthfirst approach introduces a shift toward autonomous agentic systems. Unlike previous models that might offer theoretical analysis, this agentic system focuses on producing concrete, reproducible PoC inputs to confirm its findings.
By utilizing commercially available models rather than proprietary ones like Mythos, the depthfirst team demonstrated that deep scans of large codebases are becoming more accessible. The system's ability to find critical bugs that were missed by previous high-profile AI audits suggests that the architecture of the security agent—specifically its ability to perform deep, iterative scans—is as important as the underlying model's reasoning capabilities. This represents a transition from AI as a simple assistant to AI as a production-ready autonomous security researcher.
Economic and Technical Implications of Automated Exploitation
One of the most striking aspects of this discovery is the economic efficiency of the AI agent. The research notes a cost of $1,000 for the discovery and validation process, which is significantly lower than the $10,000 associated with other methodologies. This reduction in cost, combined with the speed of discovery, suggests a fundamental shift in the economics of vulnerability research.
Furthermore, the development of a Proof of Concept demonstrating a Remote Code Execution (RCE) exploit primitive is a critical technical milestone. In the context of FFmpeg, which is often used to process media in a "zero-click" environment (where a user does not need to interact with a file for the exploit to trigger), the existence of RCE primitives poses a severe threat. The ability of an AI agent to not only find a bug but also demonstrate its exploitability changes the landscape of how software maintainers must respond to automated security findings.
Industry Impact
The discovery of 21 zero-days in a library as foundational as FFmpeg has immediate implications for the global software supply chain. Because FFmpeg is integrated into nearly every major browser and streaming service, these vulnerabilities represent a broad attack surface that could affect billions of users. The industry must now grapple with the reality that AI agents can uncover flaws that have survived 20 years of human and algorithmic oversight.
For the AI industry, this success validates the use of agentic systems in complex software engineering tasks. It proves that AI can handle the nuances of heavily optimized C code and provide actionable security intelligence. For the cybersecurity sector, it signals an era where the speed of vulnerability discovery may accelerate beyond the capacity of manual patching cycles, necessitating more automated and robust defense mechanisms.
Frequently Asked Questions
Question: How does the depthfirst agent differ from Google's Big Sleep?
While Google's Big Sleep team focused on identifying 13 vulnerabilities, the depthfirst agent identified 21 zero-days and emphasized the creation of concrete, reproducible PoC inputs. Additionally, depthfirst achieved these results using available models at a significantly lower cost ($1k vs $10k).
Question: Why were these vulnerabilities able to remain hidden for 20 years?
FFmpeg's codebase is extremely large (1.5 million lines) and written in complex, optimized C. Despite decades of fuzzing and manual audits, the deep reasoning capabilities of modern AI agents allowed for the discovery of latent issues that traditional tools and human reviewers missed.
Question: What is the significance of a "zero-click" attack in FFmpeg?
FFmpeg is often used by infrastructure to automatically process media files. A zero-click attack means a vulnerability could be exploited simply by a system parsing a malicious file without any direct user interaction, making it a highly dangerous category of security flaw.