Shai-Hulud Malware Discovered in PyTorch Lightning AI Training Library: Critical Security Alert for PyPI Package Users
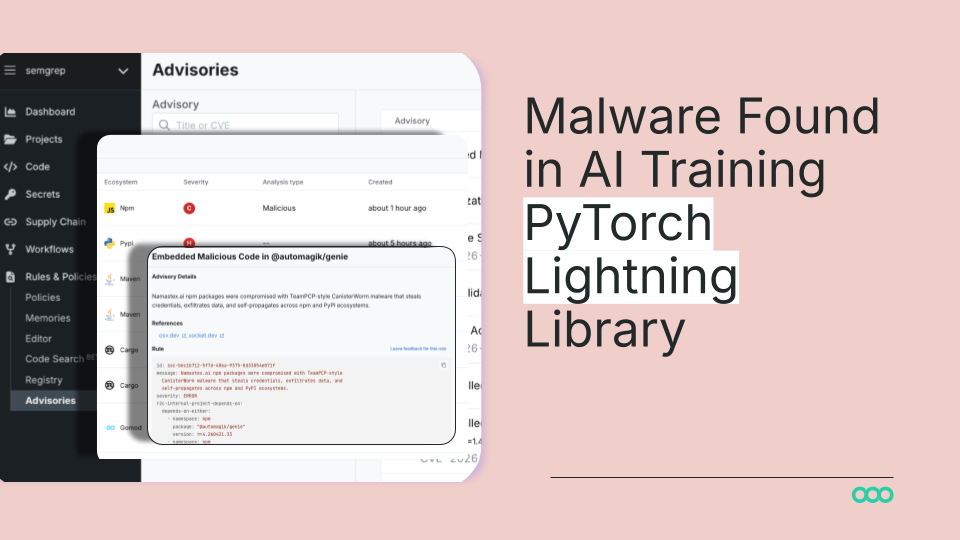
A significant security breach has been identified in the popular PyTorch Lightning AI training library, specifically affecting the 'lightning' package hosted on PyPI. Security researchers at Semgrep have uncovered malicious code themed after 'Shai-Hulud' within versions 2.6.2 and 2.6.3 of the library. This malware is engineered to execute immediately upon the package being imported, with the primary objective of stealing user credentials. The discovery was highlighted during the RSA conference, coinciding with the launch of new AI-driven security detection tools. Developers and AI researchers utilizing these specific versions are urged to audit their environments and update their dependencies immediately to mitigate the risk of credential theft. This incident underscores the persistent and evolving threats within the AI software supply chain.
Key Takeaways
- Affected Versions: The compromise specifically impacts versions 2.6.2 and 2.6.3 of the
lightningpackage on the Python Package Index (PyPI). - Malware Theme: The malicious code is identified as 'Mini Shai-Hulud' themed, referencing the iconic desert creatures from the Dune universe.
- Execution Method: The malware is designed to trigger automatically upon import, meaning simply calling
import lightningin a script activates the malicious payload. - Primary Threat: The core function of the malware is to steal credentials from the host system where the AI training library is being used.
- Discovery Context: The threat was identified by Semgrep and announced in conjunction with their RSA conference activities and the launch of Semgrep Multimodal.
In-Depth Analysis
The Compromise of the Lightning PyPI Package
The discovery of malicious code within the lightning package represents a targeted attack on the AI development community. PyTorch Lightning is a widely adopted framework designed to streamline the training of complex AI models, making it a high-value target for supply chain attacks. According to the research, the compromise was injected into versions 2.6.2 and 2.6.3.
By infiltrating a core dependency used in AI research and production, the attackers gained a foothold in environments that often handle sensitive data and high-compute resources. The use of the PyPI ecosystem as a distribution vector highlights the ongoing vulnerability of open-source repositories to package hijacking or malicious injections. This specific incident demonstrates that even established libraries with significant user bases are not immune to sophisticated supply chain compromises.
Execution Mechanism and the Shai-Hulud Theme
The malware, dubbed with a 'Mini Shai-Hulud' theme, utilizes a particularly aggressive execution strategy. Unlike malware that requires a specific function to be called, this code executes on import. In the context of Python development, this means that as soon as a developer or an automated pipeline attempts to use the library, the credential-stealing routine begins.
This 'on import' execution is a hallmark of high-impact supply chain malware, as it minimizes the time between infection and execution. The primary goal of this specific payload is the theft of credentials. While the original report does not specify the exact nature of the credentials targeted, in an AI training context, this often includes environment variables, API keys, or access tokens used to manage cloud infrastructure and data repositories. The thematic naming suggests a level of customization or branding by the threat actors, a trend increasingly seen in modern malware campaigns.
Industry Impact
AI Software Supply Chain Vulnerabilities
This incident serves as a critical warning for the AI industry regarding the security of its software supply chain. As AI development becomes more decentralized and reliant on a vast web of open-source dependencies, the surface area for attacks grows. The compromise of a foundational tool like PyTorch Lightning indicates that attackers are moving 'upstream' to infect the very tools used to build modern technology.
For organizations, this highlights the necessity of moving beyond simple version pinning. It requires the implementation of Secure Guardrails and automated scanning of open-source dependencies. The fact that this was discovered by Semgrep using advanced detection methods—such as those found in their Supply Chain and Multimodal products—suggests that traditional static analysis may no longer be sufficient to catch sophisticated, themed malware hidden within complex libraries.
The Shift Toward AI-Enhanced Security Detection
The timing of this discovery, coinciding with the launch of Semgrep Multimodal, points toward a shift in how the industry must defend itself. By combining AI reasoning with rule-based detection, security tools are evolving to identify patterns that human reviewers or simple scripts might miss.
As AI models are used to write code (a concept referred to as 'Vibe Coding' in the industry), the need for automated security pipelines that can combine static analysis with AI at scale becomes paramount. This breach reinforces the importance of Static Application Security Testing (SAST) and Semantic Analysis in identifying hardcoded secrets and malicious logic before they can be deployed into production environments. The industry must now prioritize securing the code, regardless of who—or what—writes it.
Frequently Asked Questions
Question: Which specific versions of the PyTorch Lightning library are compromised?
According to the security research, the malicious code was found in versions 2.6.2 and 2.6.3 of the lightning package on PyPI. Users should check their requirements.txt or environment files to ensure they are not using these specific versions.
Question: How does the Shai-Hulud malware infect a system?
The malware is designed to execute on import. This means that the moment a user runs a Python script containing the statement import lightning, the malicious code is triggered. It does not require the user to call any specific malicious function to begin its credential-stealing activities.
Question: What is the main objective of this malicious code?
The primary objective of the Shai-Hulud themed malware is to steal credentials. In the environment of an AI developer, this could potentially include sensitive access keys, tokens, or other authentication data stored on the system or within environment variables.